 TrustnGo
Cyber Resilience Act
The Cyber Resilience Act (CRA) is a new EU regulation ensuring that all products with digital elements (hardware or purely software) are secure by design and throughout their lifecycle.
Key requirements include risk management, timely security patches and incident reporting. From December 2027, products placed on the EU market must comply and display CE certification marks for cybersecurity conformity. Benefits include stronger consumer confidence and standardized European security practices.
TrustnGo provides consulting, assessment and testing to help your organization meet CRA requirements before the December 2027 deadline. Two paths are available: we handle compliance end to end, or we review your technical file before you sign it.
Two paths
The right path depends on how far along you are. If you are starting from scratch or your teams are short on time, we run the compliance work with you, from mapping to demonstrating conformity. If your technical file already exists, we read it the way an assessor would, before the EU declaration of conformity or submission to a notified body.
End-to-end CRA support
A one-stop shop, from mapping to CE marking
We take on the whole process, first at organization level and then for each product, through to the technical documentation and the tests that demonstrate conformity.
Our six-step approach
- 01
Mapping products and processes
Lists products and processes of the organization to obtain a clear view on how the organization operates and what kind of products or services it sells.
- 02
Gap analysis at organizational level
Use the previous mappings to perform a gap analysis versus the general essential requirements of the CRA at organization level (Secure Development Life Cycle, product life-cycle, vulnerability management, etc.).
- 03
Define a compliance roadmap
Define a compliance roadmap at the organization level including setting up a compliant SDLC and life-cycle management as well as establishing a training plan to help technical people to improve their skills.
- 04
Risk & gap analysis at product level
Now the implementation of the compliance roadmap is on the rail at organization level, tackle the problem at product level by identifying the technical gaps that really need to be filled to comply with CRA essential requirements.
- 05
Fix the gaps with our advice
Actually fix the gaps by effectively deploying new processes and methodologies. Also, prepare check-lists mapping general standard requirements to product specific requirements that can be efficiently and repeatedly implemented by dev teams across all the products.
- 06
Demonstrate compliance
Write supporting technical documentation and carry out penetration tests on products, web interfaces or backends, and mobile applications.
The fixed price depends on the number of products, their class and the maturity of your processes. We set it after an initial 45-minute call.
Independent CRA review
A second pair of eyes before you sign
Under self-assessment, the EU declaration of conformity rests on a file that nobody outside your company has read. The most common gaps are not forgotten requirements but missing links: a risk with no requirement against it, a requirement set aside without justification, a test that does not cover what the report concludes.
We read your file the way an assessor would, before signature, and hand you a ranked list of findings with the expected action for each one.
Three scopes, contracted separately
Scope
Technical documentation
What the review covers
- Completeness of the file
- Risk analysis and traceability to the selected requirements
- Justification of requirements set aside
- SBOM
- User information
- Support period
- Draft declaration
Scope
Test reports
What the review covers
- Coverage of the test plan against the applied standard
- Relevance of the methods
- Sufficiency of the evidence
- Justification of verdicts and non-applicability claims
Scope
Complete file
What the review covers
- Technical documentation review
- Test reports review
- Consistency between risks, requirements, tests and declaration
These fixed prices apply to default-class products. For important class I or class II products, the review is quoted separately. Each package includes a second reading after your corrections. Beyond two products or three variants in the same file, the scope is quoted separately.
What you receive
- A review report, in French or English, with each finding rated blocking, major or minor, linked to the requirement concerned and paired with the expected action.
- A one-page summary to decide internally before signing.
- A second reading after corrections.
How it works
- 1.A 45-minute call to qualify the product, its category, the applied standard and the state of the file.
- 2.Confirmation of the scope and the package.
- 3.Transfer of the file and review.
- 4.One-hour debrief by video call.
- 5.Second reading after your corrections.
The review and the remediation are two separate services. If you would like us to work through the findings with you, that support is billed on a time and materials basis, on quotation.
Disclaimer
The review is not a certification and TrustnGo is not a notified body. It is intended for products the manufacturer can assess itself. Where a notified body is required, the same review serves as preparation for that assessment.
Discover Our Key Strengths
One-Stop Shop
From initial audit to full CRA compliance, TrustnGo handles the entire process including gap analysis, technical advice, documentation writing & pentests.
Integrated Technical & Regulatory Expertise
TrustnGo combines deep knowledge of EU cybersecurity regulations with hands-on experience in securing digital products.
Time Savings and Risk Reduction
By anticipating CRA obligations, you secure your products early, minimize compliance risks and costs, and strengthen customer and partner confidence in your brand.
Why choose TrustnGo
Securing an embedded device can be a challenge and demonstrating this security is another one.
During the past years, the EU has severely tightened cybersecurity requirements for IoT & embedded devices. NIS2, RED Directive, CRA, Regulation of machinery, … TrustnGo follows all these topics and has developed a comprehensive and cost-effective methodology based on our expertise in EN 303 645, EN 18031, IEC 62443, etc.
As a one-stop-shop, we also deliver technical advice on how to implement security functions, and we perform penetration testing to assess the robustness of your implementation.
We can act not only at the product level but also at the company level to achieve sustainable and reproducible compliance.
Example Case
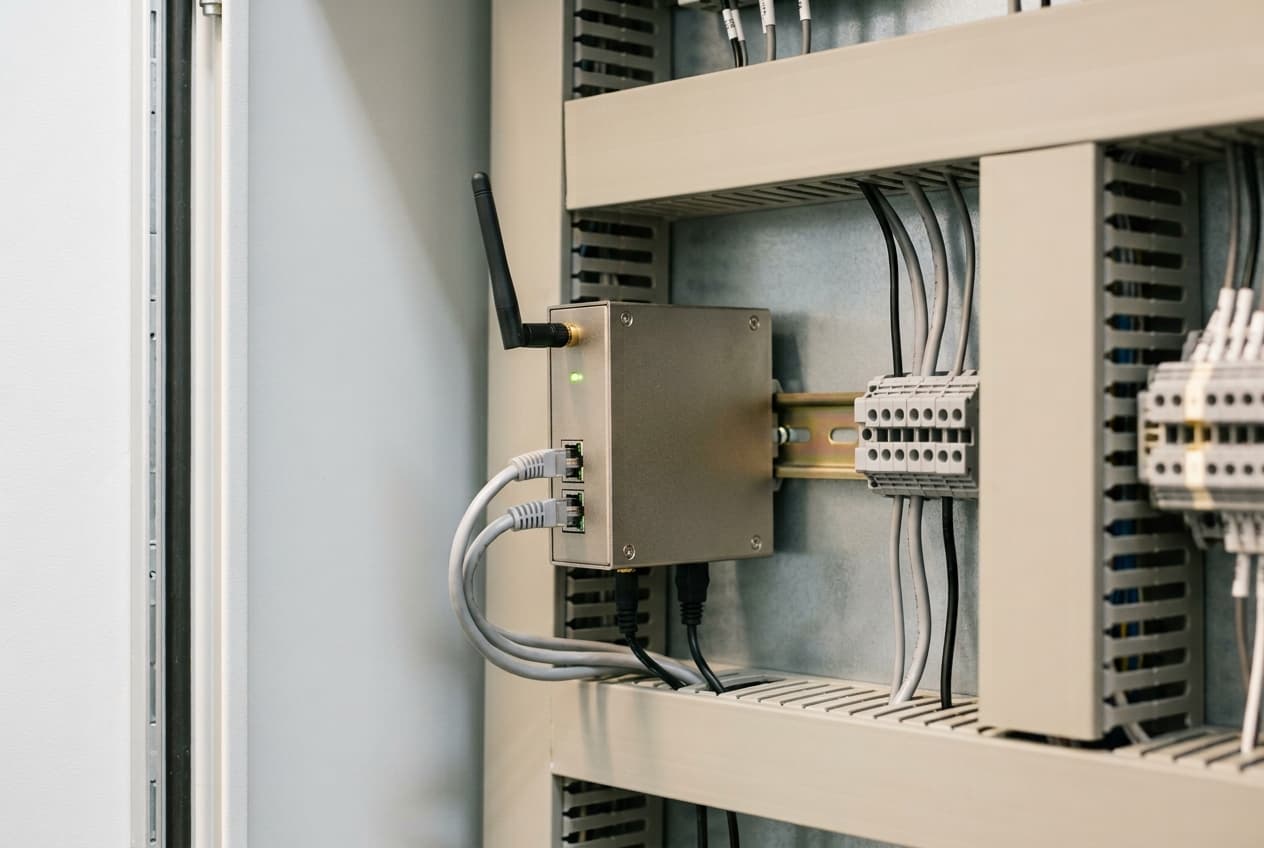
A company selling solutions embedding a custom internet gateway, with wireless interfaces and already compliant to EN 18031-1/2, wants to comply with CRA requirements.
The solution is considered as a whole, including the web interfaces, the backend and the related mobile application. A risk & gap analysis is conducted and the EN 18031's evidence are completed to demonstrate the conformity of the solution.
In addition, a secure development life cycle is deployed at company level and vulnerability management is fully integrated to the company's processes.